Security research · Responsible disclosure · October 2026
Responsible Disclosure: Two Security Vulnerabilities on pbinfo.ro
This article documents two vulnerabilities I identified and reported privately to pbinfo.ro: a Stored Cross-Site Scripting issue in article titles and a server-side file disclosure issue in the code-evaluation pipeline.
Disclosure timeline
- 29 July 2026: Stored XSS discovered and privately reported.
- After reporting: The maintainer confirmed that the XSS issue had been corrected.
- Follow-up: I asked whether I could publish a short technical article after remediation.
- Maintainer response: I was asked to delay publication in case additional issues were identified and fixed first.
- 29 September 2026: A second vulnerability involving compiler diagnostics and server-side file disclosure was discovered and privately reported.
- 30 September 2026: The maintainer confirmed that the exposed data belonged to the virtual machine used by the evaluation system and said compilation would also be moved into an isolated environment.
- 1 October 2026: The second vulnerability was confirmed fixed.
Finding 1
Stored XSS in article and sub-article titles
The first vulnerability affected the title field used when creating an article or sub-article. A harmless browser alert was used to confirm that user-controlled JavaScript could be stored and executed when the resulting page was viewed.
- Discovered
- 29 July 2026
- Class
- Stored Cross-Site Scripting (Stored XSS)
- Affected functionality
- Article/sub-article title creation
- Status
- Reported and confirmed remediated
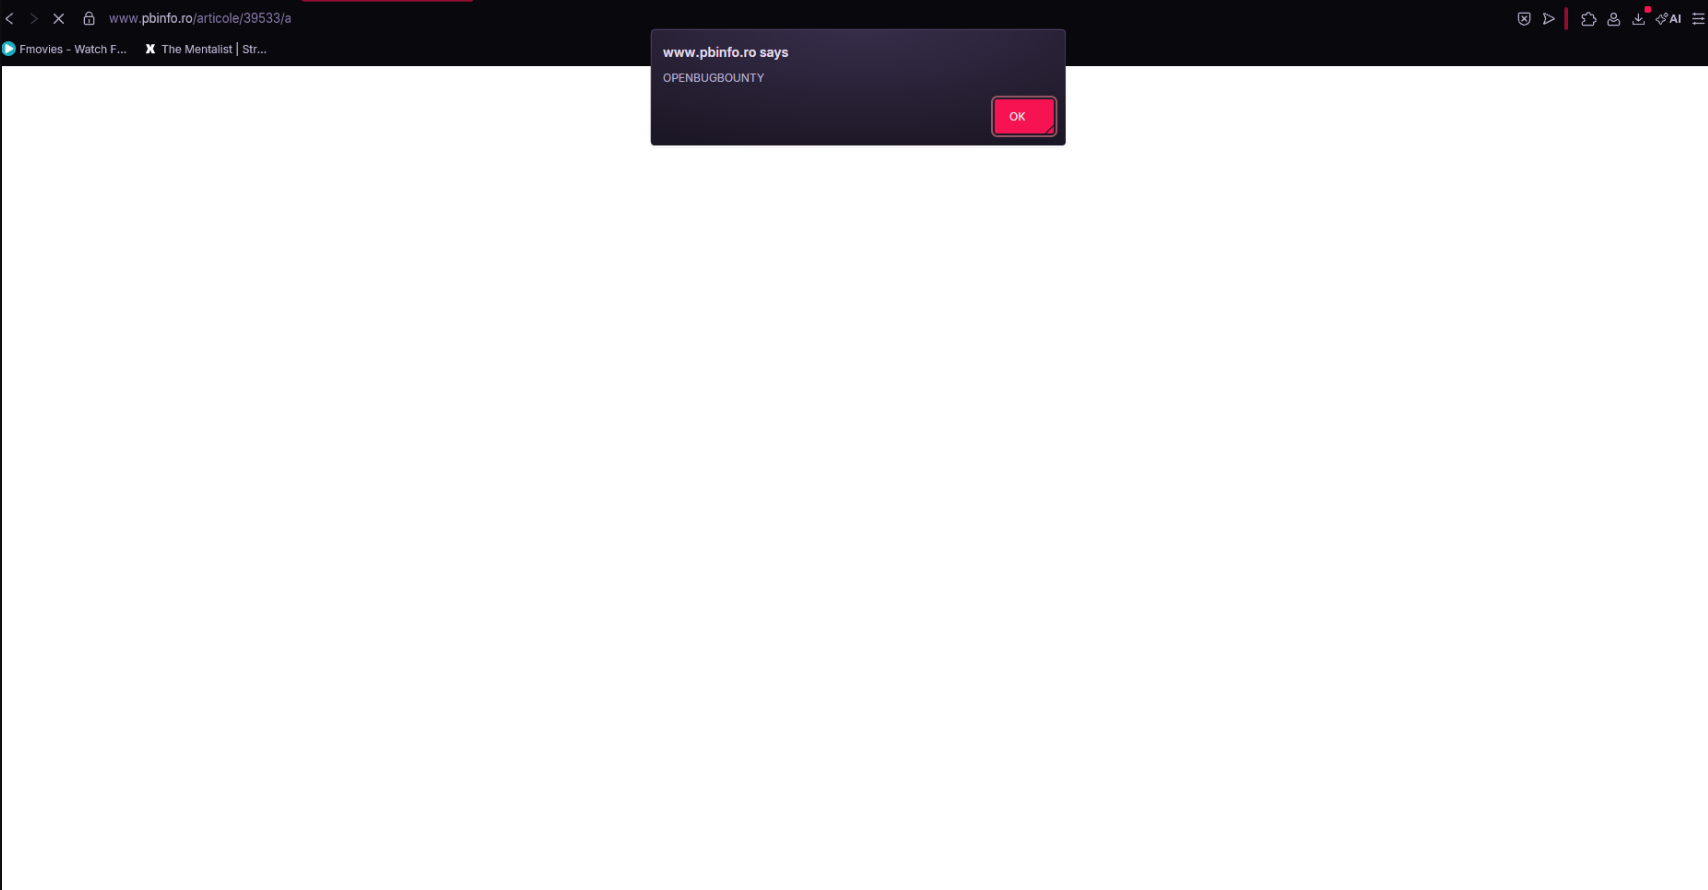
Impact and disclosure
Because the payload was persistent, a malicious payload could potentially have affected other visitors to the page. Higher-impact behavior was not tested. I reported the vulnerability privately before publishing any details, and the maintainer corrected the issue.
Finding 2
Server-side file disclosure through compiler diagnostics
The second issue was found in the platform's code-evaluation functionality. Compiler diagnostic behavior could be influenced in a way that exposed content from a referenced server-side file. I used only a non-sensitive, normally world-readable system file to confirm the behavior and stopped testing after establishing the issue.
- Discovered
- 29 September 2026
- Class
- Arbitrary file read / server-side file disclosure via compiler diagnostics
- Access required
- An authenticated user able to submit code for compilation
- Status
- Reported, acknowledged, and confirmed fixed
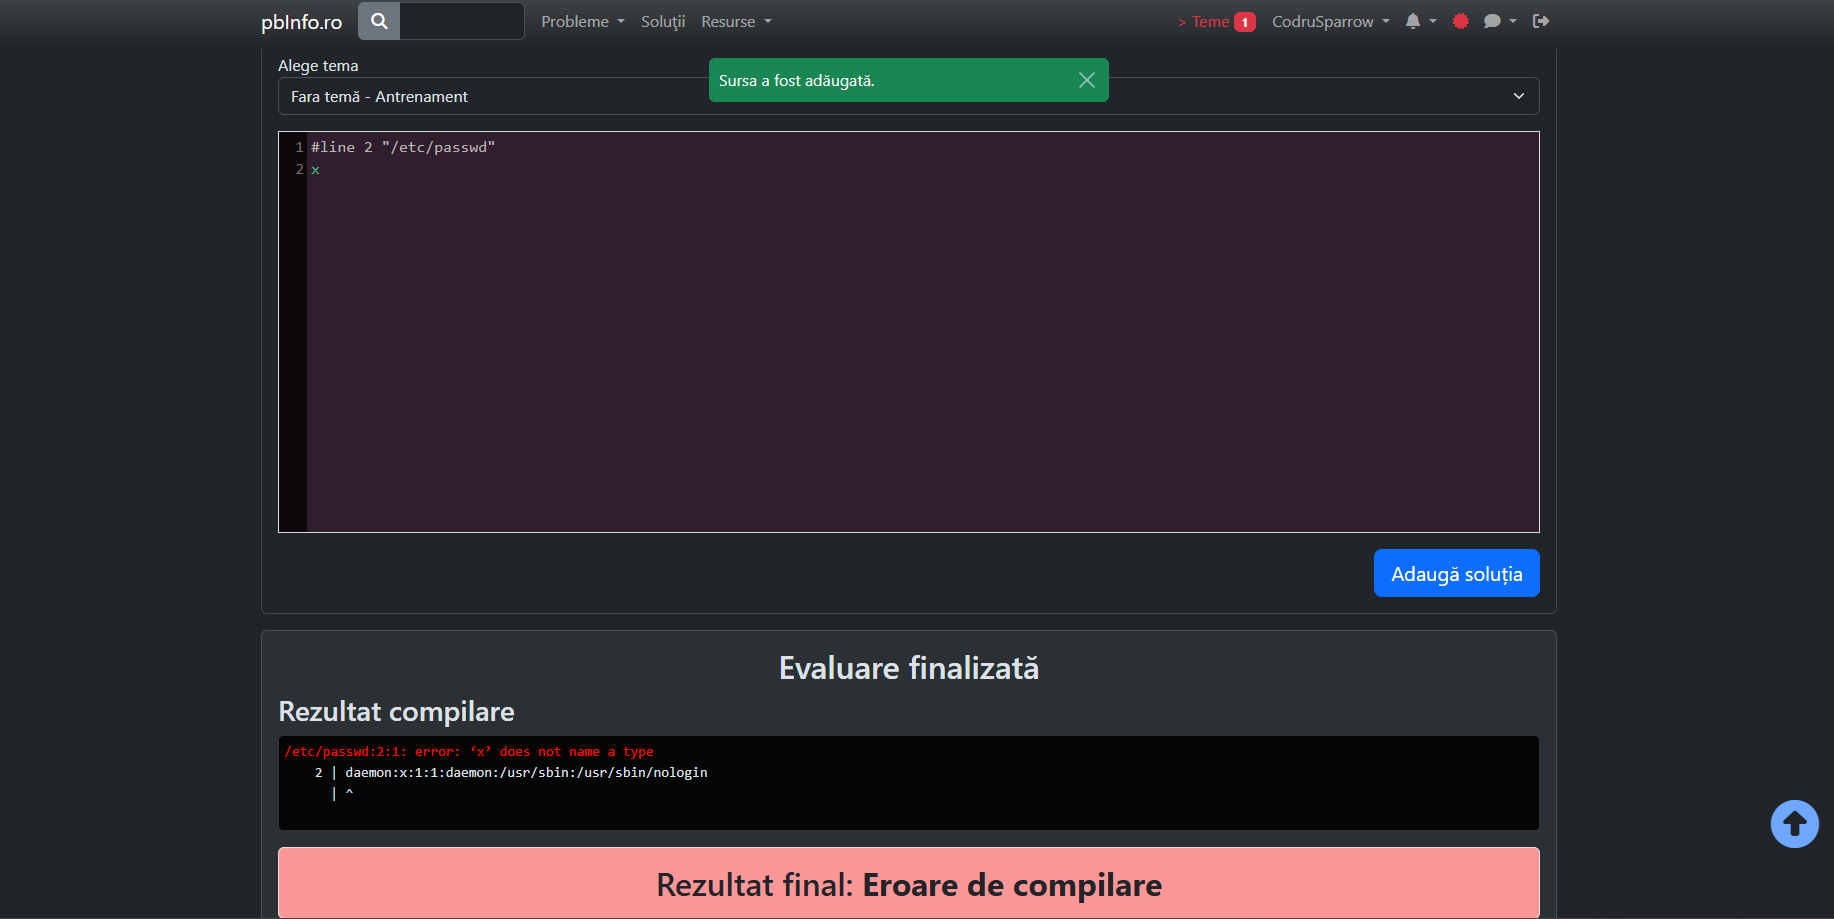
Maintainer response and remediation
The maintainer confirmed that the exposed data belonged to the virtual machine on which the evaluation system runs. He also stated that the compilation stage would be changed to run in an isolated environment, in the same way that submitted programs were already isolated during execution. The vulnerability was subsequently confirmed fixed.
Testing boundaries
Both findings were tested conservatively. I did not access other users' data, test private configuration or credential files, run automated scans, or attempt to affect service availability.
Why I am publishing this
The goal of this write-up is to document the research and responsible-disclosure process, not to enable abuse. Both findings were reported privately before public discussion, both were remediated before publication, and the write-up intentionally omits details that were unnecessary or that the maintainer asked me not to disclose.
Acknowledgement
Thanks to the pbinfo.ro maintainer for responding to the reports, remediating both issues, and encouraging further responsible reporting.
Back to blog